The finding to use
Set up and understand recovery before you depend on a new sign-in method.
Sources checked 14 November 2026. Follow the reasoning, then use the worksheet for your own situation.
01 / Tomorrow Matters
Start with the lost-phone question
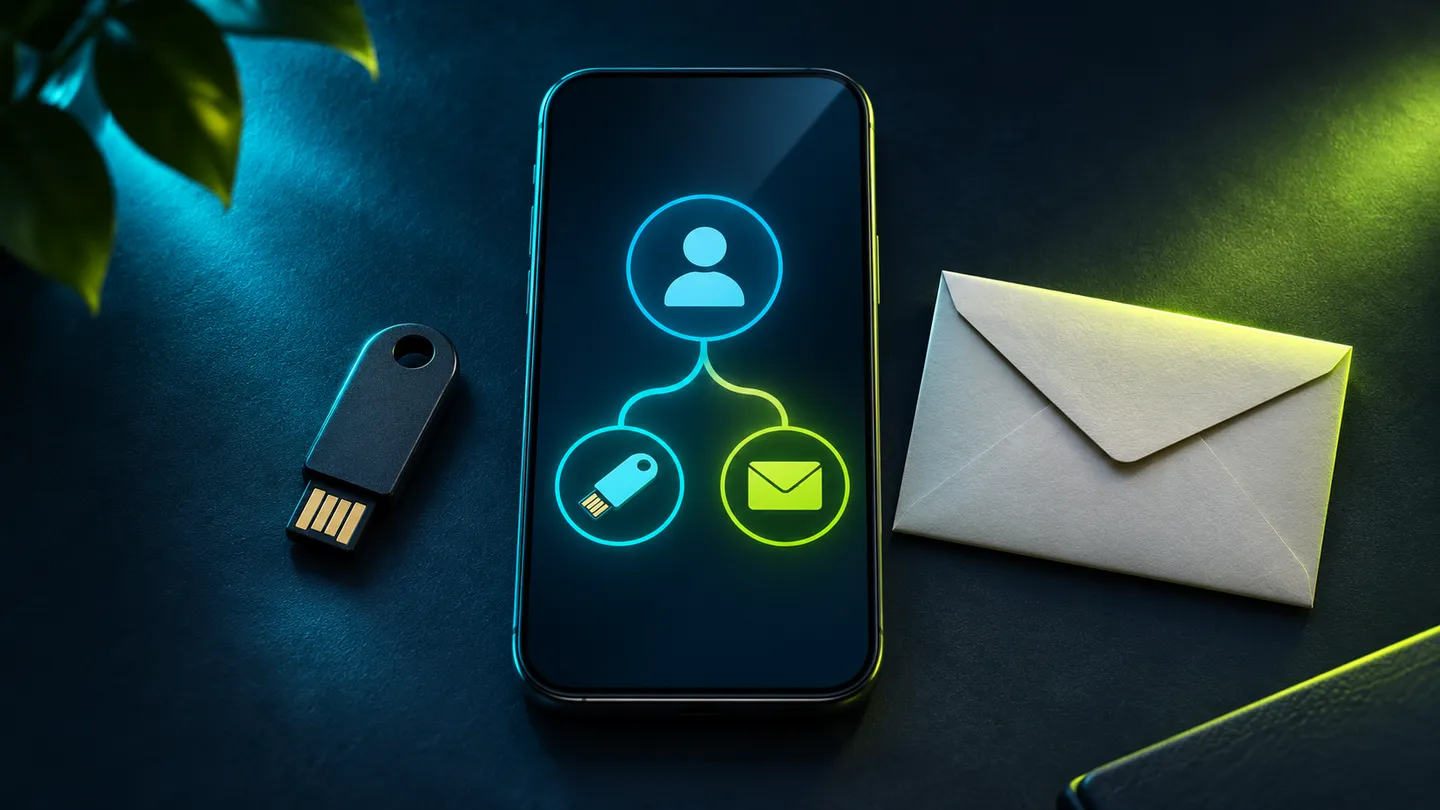
You replace a phone, open an important account and discover you do not know where its passkey was stored. Was it synced through a password manager? Kept on that device? Attached to a security key you left elsewhere?
You want those answers before the old phone disappears.
Passkeys change how you sign in. FIDO describes them as phishing-resistant credentials using public-key cryptography, typically approved through a device unlock method. They may be synced through a provider or bound to a device. [1] Those differences matter to recovery even when the sign-in screens look similar.
This guide is a planning checklist. It does not claim that every service offers the same recovery options, or that a stronger login method makes the whole account immune to compromise.
02 / Tomorrow Matters
Identify the provider behind the prompt
Next time a service offers to save a passkey, read which provider or device is handling it. Do not treat “saved on my phone” as the complete description. The credential may depend on an account whose own recovery process you also need to understand.
Record the service, credential provider, devices you expect to use and the official help page. Keep this inventory free of passwords, recovery codes and other secrets. It should help you find the procedure without becoming a way into your accounts.
For a work or school account, check the organization’s instructions. An administrator may require managed devices or particular authenticators. Your personal preference does not override those rules.
If the setup uses a separate security key, decide where the key is kept and what happens when it is unavailable. If it uses sync, learn how you would regain access to the provider. Avoid assuming that owning a replacement phone settles either question.
03 / Tomorrow Matters
Review recovery as its own route into the account
Google says adding a passkey does not remove the authentication or recovery factors already on the account. [2] Switching your normal login experience therefore does not finish your account review.
Look at the settings that actually exist: recovery contacts, other authenticators, signed-in devices and any documented backup method. Check that contact details still belong to you. A number you have given up is not a reliable plan simply because it remains listed.
Do this while your current sign-in works. Read the official instructions rather than relying on a remembered setup screen. Requirements can differ by account and can change over time.
Think through a specific failure: the phone is lost while you are away from home. Which available device or documented recovery method would you use? If every answer starts with “I need the lost phone”, the plan needs more work before you depend on it.
04 / Tomorrow Matters
Shared computers change the trust decision
On a shared laptop, stop before creating a personal passkey. Google warns that someone able to unlock a device can use its passkey to access the account, even after you sign out. [2] A signed-out browser is not the same boundary as a privately controlled device.
A family computer, a borrowed laptop and your own phone have different users and access patterns. Read the prompt carefully so that a convenient setup does not leave a personal credential somewhere you did not intend.
Do not approve an unexpected sign-in request because a caller says they are helping you recover an account. Go to the service through a route you recognize and follow its official process. Keep recovery material private rather than pasting it into a support chat or a planning document.
Local device security still matters. A passkey cannot make it safe to leave an unlocked device with someone you do not trust.
05 / Tomorrow Matters
Rehearse a replacement without destroying your working setup
Before changing phones, use the service’s documented process to confirm how the replacement device will sign in. Keep the old device and current credentials available during setup. Do not delete your only working credential as an experiment.
If you cannot complete a safe check, write down the unresolved step and consult the official guidance. Recovery is a poor place to improvise. An employer-managed account may require administrator support instead of the personal-account route you found online.
Google documents backup sign-in and recovery options separately. [3] Use the instructions appropriate to your account. After recovering from a loss, review the lost device’s access and remove the relevant passkey or sessions as the service directs.
Record what you have confirmed and when. A checklist you last reviewed before changing numbers, jobs and devices may no longer describe the account you have now.
06 / Tomorrow Matters
Keep a short recovery checklist
Can you identify the credential provider? Do you know whether the passkey syncs or stays with a device? Can you find an official recovery route without a link from a stranger? Are recovery contacts current? Have you kept personal credentials away from shared devices?
Store any recovery material according to the provider’s guidance, with access that does not depend entirely on the device you might lose. Review the plan after a phone change, number change or departure from an organization.
The next time a sign-in takes only a fingerprint, take a moment to check the less convenient path too. Fast access on a good day is useful. Knowing what to do on a bad day is what makes the setup practical.
Passkey recovery inventory
| Record without secrets | Find out | Review after |
|---|---|---|
| Credential provider | Where the credential is managed | Phone or provider change |
| Credential type | Synced or device-bound | New device setup |
| Official recovery route | Requirements for your account | Number or recovery contact change |
| Shared-device exposure | Who can unlock the device | Sharing or retiring hardware |
Sources & revision note
Primary sources checked 2026-11-14. Practical frameworks are editorial guidance; illustrative examples are not measured results.
- FIDO Alliance: passkeys
- Google Account: sign in with a passkey
- Google Account: backup sign-in and recovery
Revision 2 · 2026-11-14: Rewritten with clearer examples, a practical worksheet and a stronger decision checklist.
Keep the useful part
Take the decision back to your work.
Set up and understand recovery before you depend on a new sign-in method.
This preference is private to this browser, not a public vote count.